Patch Once, Rebuild Everywhere: A Distroless Base Image Pipeline
Table of Contents
- The Problem: N containers, one CVE
- What I Had
- Naaa… the alternatives
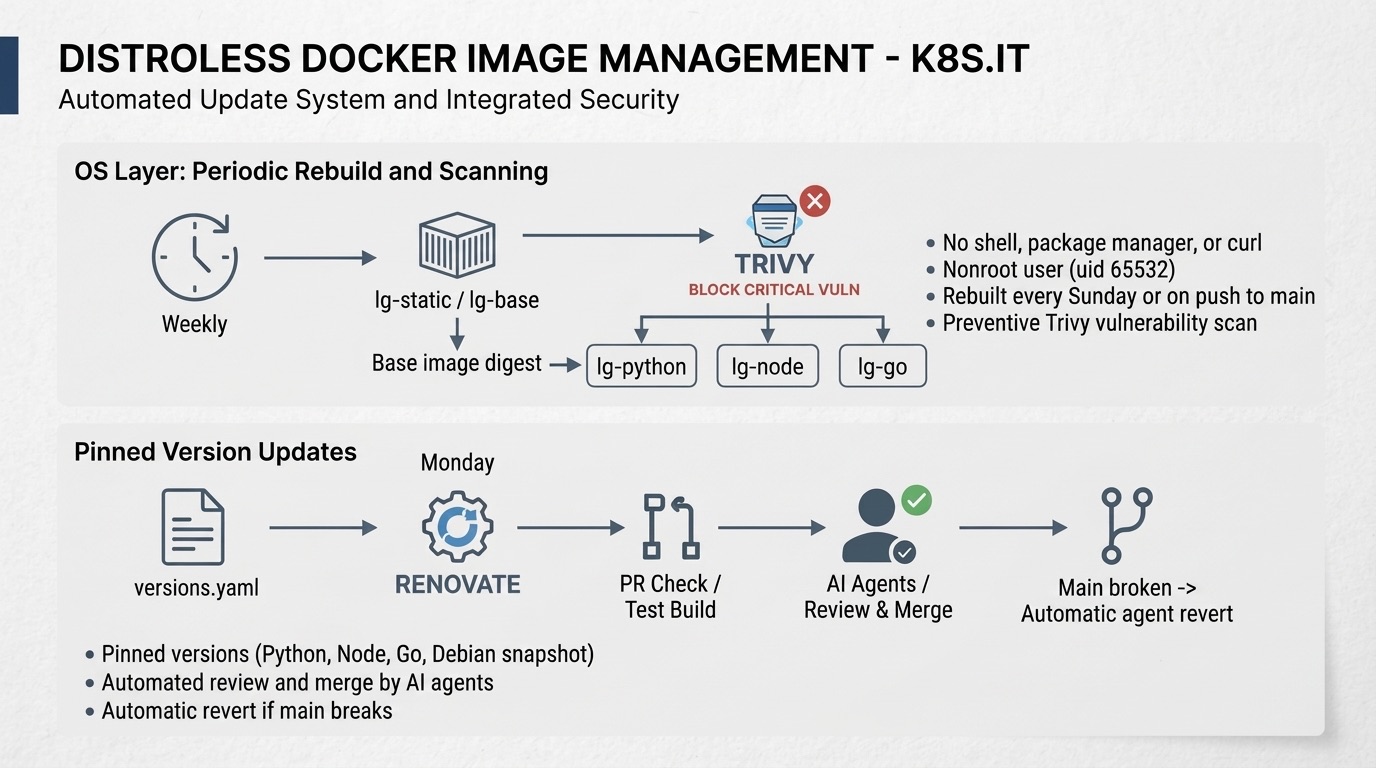
- The Idea: Layers That Patch Themselves
- Building a Distroless Base Without Google
- The Single Source of Versions
- The Cascade
- Trivy as the Gate
- Who Keeps It Alive: Renovate and the Agents
- The Test: pytbak on the New Base
- What Broke on the Way
- Security Considerations
- Monitoring and Observability
- Conclusion
- Reflections
Here we are.
Last week I scanned pytbak, my debug/test API, with Trivy. The release I had been running for a long time, lgirardi/pytbak:v2.0.3, sat on Debian 12.9 and the report said 842 vulnerabilities, 16 of them CRITICAL. So I did the obvious thing: I updated. New release, v2.0.425, rebuilt on the current public python:3.15.2-slim (Debian 13.7). The count dropped to 444, 4 of them CRITICAL. Better, and still not good.